SecurityQA/Testing & Reliability
User Enumeration Vulnerabilities in Login Forms: How to Protect Web Applications From Account Discovery Attacks
 Joaquin Moreira||Read 5 minJoaquin Moreira||Read 5 min
Modern web application security often focuses heavily on major vulnerabilities such as SQL injection, cross-site scripting (XSS), or remote code execution. However, some of the most overlooked security weaknesses are the subtle information leaks that help attackers map and target systems more effectively.
One of the most common examples is user enumeration.
At Blue Trail Software, we believe secure software development requires attention not only to critical exploits, but also to smaller weaknesses that attackers frequently combine into larger attack chains. User enumeration vulnerabilities may appear minor on the surface, but they can significantly increase the effectiveness of brute force attacks, credential stuffing, phishing campaigns, and account targeting efforts.
User enumeration occurs when an application unintentionally reveals whether a username, email address, or account exists within the system. In practice, this means an attacker can ask:
“Does this user have an account here?”
and the application accidentally provides the answer through:
error messages
response timing
registration feedback
password reset behavior
authentication workflows
Although this may seem harmless, even small pieces of information can become valuable to attackers when combined with other vulnerabilities or leaked credentials.
User enumeration significantly improves the efficiency of several common cyberattacks. Attackers can use valid account information to:
launch credential stuffing attacks
perform brute force login attempts
create targeted phishing campaigns
identify high-value users
validate leaked credentials from previous breaches
map organizational accounts and employee identities
In sensitive systems, simply confirming account existence may expose users to additional risk. For example:
healthcare platforms
financial systems
enterprise software
whistleblower portals
internal business applications
may all contain accounts where anonymity or privacy is critical.

User enumeration vulnerabilities typically appear in authentication and account-management workflows.
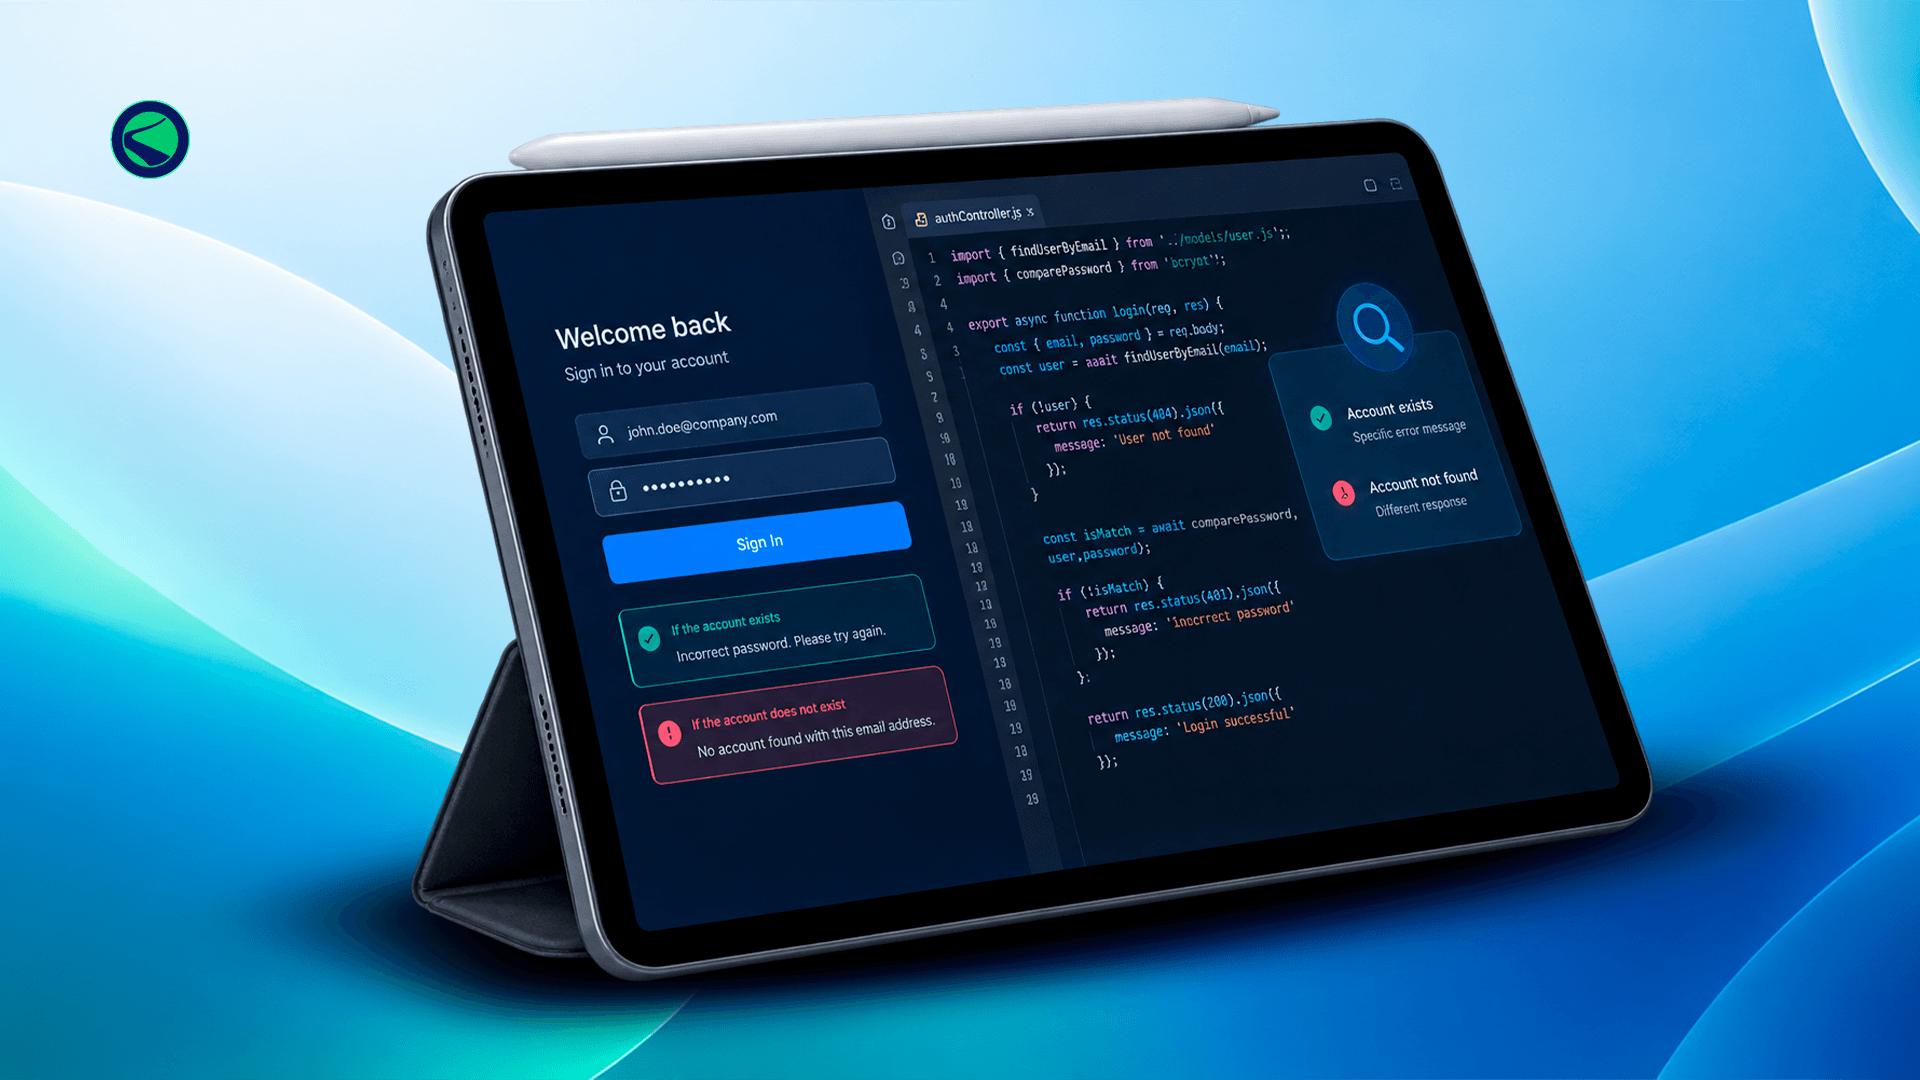
The most common source is login forms that provide different responses depending on whether a username exists.
“Username does not exist” vs. “Incorrect password”
This confirms which accounts are valid.
“Invalid username or password”
Using generic authentication error messages prevents attackers from distinguishing valid accounts from invalid ones.
Password recovery flows frequently expose account existence.
“No account found with this email address”
“If an account exists, recovery instructions have been sent”
This prevents attackers from validating email addresses through password reset functionality.
Registration systems can also unintentionally reveal existing users.
“Username already taken”
Generic registration messaging combined with separate validation or notification workflows
While usability and UX considerations matter, security-sensitive systems may require additional safeguards to prevent automated account discovery.
Even when applications use generic error messages, user enumeration can still occur through timing differences. For example:
valid usernames may trigger database lookups
password hashing may take longer for existing accounts
email generation may create slower responses for real users
Attackers can measure these response time differences to determine whether accounts exist. This technique is commonly referred to as a timing attack.
At Blue Trail Software, security testing includes evaluating not only visible responses but also backend behavior that may unintentionally leak sensitive information.
User enumeration often increases the effectiveness of two major attack types.
Credential stuffing uses stolen username/password combinations from previous data breaches to attempt automated logins across multiple platforms.
Because many users reuse passwords, attackers can successfully compromise accounts when valid usernames are known.
Brute force attacks systematically test multiple password combinations against known usernames.
User enumeration helps attackers focus only on confirmed accounts, making these attacks more efficient and difficult to detect early.
Security-focused QA processes should include user enumeration testing across all authentication-related workflows. Teams should evaluate:
login forms
registration systems
password reset flows
account recovery functionality
API authentication responses
timing consistency
error message behavior
Testing should compare:
valid vs invalid usernames
valid vs invalid email addresses
response timing differences
authentication response structures
At Blue Trail Software, security testing increasingly involves collaboration between QA engineers, developers, and DevSecOps teams to identify subtle vulnerabilities before production release.

Organizations can reduce user enumeration risks through several practical security measures.
Authentication systems should avoid revealing whether:
usernames exist
passwords are incorrect
emails are registered
Consistent messaging reduces information leakage.
Applications should process authentication requests with similar timing behavior regardless of account validity.
Artificial delays may sometimes be necessary to reduce timing attack exposure.
For example:
password reset requests can always trigger a visible success message
backend workflows can remain identical regardless of account existence
This helps prevent behavioral differences attackers can measure.
Rate limiting helps prevent automated enumeration attempts by restricting repeated requests from the same source.
CAPTCHA and anti-automation protections help reduce large-scale account discovery attacks.
Progressively increasing authentication delays after repeated failed attempts makes brute force attacks significantly less practical.
For example:
1-second delay
2-second delay
4-second delay
8-second delay
This dramatically increases the time required for automated attacks.
Authentication systems are among the most heavily targeted areas of modern applications.
Even seemingly minor weaknesses can:
expose user information
increase attack efficiency
weaken account security
support larger attack chains
Secure authentication design requires attention to:
usability
performance
privacy
security consistency
backend behavior
user experience
Organizations that proactively address subtle vulnerabilities improve their overall security posture and reduce unnecessary exposure.
User enumeration vulnerabilities may not appear as dramatic as major injection or execution flaws, but they can provide attackers with valuable reconnaissance information that significantly increases the effectiveness of larger attacks.
Preventing account discovery requires careful attention to authentication design, response consistency, and security-focused testing practices.
At Blue Trail Software, we believe strong application security depends not only on defending against critical exploits, but also on eliminating the smaller information leaks that attackers rely on to compromise systems more effectively.
User enumeration is a security vulnerability where an application unintentionally reveals whether usernames, email addresses, or accounts exist within the system.
User enumeration helps attackers identify valid accounts, improving the effectiveness of brute force attacks, credential stuffing, phishing, and targeted account attacks.
Common causes include:
different login error messages
password reset responses
registration feedback
timing differences
inconsistent authentication workflows
A timing attack measures differences in application response times to determine whether certain operations behave differently for valid vs invalid accounts.
Best practices include:
generic authentication messaging
normalized response timing
consistent request handling
rate limiting
CAPTCHA protection
exponential back-off mechanisms
Legal
2026 BlueTrail Software. All rights reserved.